🔍 Read the full analysis: How AI Helped Identify A Linux Flaw That Could Put Root Access At Risk on ThorstenMeyerAI.com

Get the latest gadgets delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
TL;DR
A How-To Geek headline says Anthropic’s Claude AI identified a Linux flaw that could allow an attacker to gain root access. The available reporting provides no vulnerability identifier, technical evidence, affected systems, confirmation from maintainers, or patch information, so the claim’s scope and severity remain unverified.
A How-To Geek headline says Anthropic’s Claude AI found a Linux flaw that could allow an attacker to gain root access, but the available reporting does not identify the vulnerability or provide technical evidence supporting the claim. Without details about affected software, exploit conditions, validation or a fix, administrators cannot determine whether their systems are at risk.
The headline characterizes the reported issue as critical and describes root access as a possible consequence. Root is the highest-privilege account on a Linux system, so a flaw that genuinely lets an attacker obtain those privileges could allow actions beyond the access normally available to a standard user. The headline alone does not establish that this impact is achievable in practice.
The source material does not name a kernel, distribution, application or software version, and it gives no vulnerability identifier or technical report. It also does not explain whether exploitation would require local access, a particular configuration or user interaction. No details are supplied about whether a human researcher reproduced the finding or how its severity was assessed.
There is also no information in the available account about maintainer notification, coordinated disclosure, an official advisory, active exploitation or a patch. The report therefore supports a narrow statement: a headline attributes a potentially serious Linux security finding to Claude. It does not establish the flaw’s scope, practical exploitability or current status.
Why Root-Level Access Matters
If independently confirmed, a vulnerability that lets an attacker obtain root privileges could have serious consequences for affected systems. Depending on the component and the conditions required to trigger the flaw, elevated access may let an attacker bypass ordinary account restrictions or alter protected system data and controls. The available source does not show that these outcomes have occurred or that the reported issue can be exploited remotely.
For system operators, the immediate issue is that the report supplies no actionable scope. Administrators cannot compare their deployments with an affected-version list or apply a targeted fix without knowing which component is involved. A headline describing a severe possible impact is not a substitute for an advisory that states who is affected and what action is required.
The attribution to Claude also puts attention on AI-assisted security research, but it does not by itself demonstrate that the vulnerability is verified. An AI system may help identify a candidate bug; determining whether it is reproducible, exploitable and correctly rated requires evidence and technical review. The distinction matters both for security teams deciding how to respond and for readers evaluating claims about AI’s role in vulnerability discovery.
Products Worth Considering

Logitech MX Keys S Wireless Keyboard, Graphite
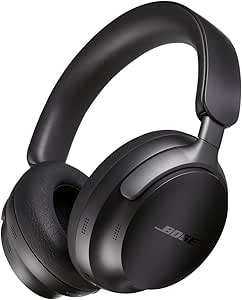
Bose QuietComfort Ultra Wireless Noise-Cancelling Headphones with Spatial Audio, Black
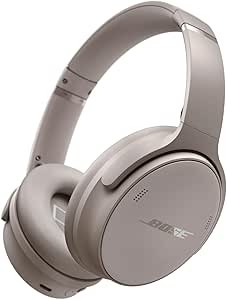
Bose QuietComfort Wireless Noise Cancelling Headphones, Sandstone
As an affiliate, we earn on qualifying purchases.
From AI Lead to Verified Vulnerability
The available source is a How-To Geek headline, with no publication date or supporting technical explanation included in the material provided. It attributes the finding to Anthropic’s Claude AI and describes a possible path to root access. The reporting available here does not establish when Claude identified the issue or what steps followed.
A candidate security finding generally needs to be examined in the relevant code and reproduced under specified conditions before its reach and impact can be assessed. A useful technical account would identify the affected component and versions, explain what an attacker must be able to do, and provide evidence for the stated impact. Where a flaw is confirmed, maintainers may issue an advisory and a fix or mitigation. None of those steps is documented in the material available for this report.
This gap does not prove that the underlying claim is false. The full report or technical details may exist elsewhere or may not yet be public, for example during a disclosure process. But that possibility is not confirmation. Until an advisory, reproducible technical account or maintainer statement is available, the reported discovery should be treated as a potential security lead, not a verified account of a critical, broadly applicable Linux vulnerability.
The Missing Technical Evidence
The central unknown is what component is affected. The source does not identify a Linux kernel, distribution, application, version range or vulnerability identifier. Without that information, it is not possible to say which systems might be exposed or whether the reported issue applies widely or only under specific conditions.
The report also does not show how the flaw could be triggered, whether it was independently reproduced, or what supports the “critical” characterization. It provides no confirmation of attacks in the wild and no information about disclosure to maintainers, an official response, a patch or temporary mitigation. These omissions prevent a reliable assessment of urgency.
It remains possible that further details are available outside the material supplied or are being withheld while a disclosure process proceeds. That possibility should not be presented as fact. At this stage, the reported potential for root access is unverified, and there is no basis here for naming affected users or recommending a specific technical remedy.
What an Advisory Must Establish
The next useful development would be a technical report or official security advisory identifying the affected component and software versions. It should describe the conditions needed to trigger the flaw and the evidence for the claimed impact, including whether the finding was reproduced and how the severity rating was determined.
A statement from relevant maintainers or the software vendor could clarify whether the issue has been confirmed and whether disclosure is underway. If a patch or mitigation is released, system operators can compare the advisory’s affected-version information with their own deployments and follow the maintainers’ instructions. No such response or fix is identified in the material available here.
Until those details are published, readers and administrators should avoid treating the headline as proof of an actively exploitable vulnerability or as evidence that a particular Linux system is affected. The story’s status may change with further reporting, but the current account does not support a reliable estimate of exposure or a specific remediation recommendation.
Key Questions
What did Claude reportedly find?
A How-To Geek headline says Anthropic’s Claude AI found a Linux flaw that could allow an attacker to gain root access. The available source material does not identify the flaw or explain how it works.
Does the report confirm that attackers are exploiting the flaw?
No. The headline describes a potential impact, but the available material does not report active exploitation or confirmed attacks.
Which Linux systems are affected?
That is not specified. The source provides no kernel, distribution, application, version range or vulnerability identifier.
Is a patch available?
The available reporting does not say whether a patch or mitigation exists. It also does not identify a maintainer advisory or response.
Is the vulnerability confirmed as critical?
The headline calls the issue critical, but no technical evidence or severity assessment is included in the available material. The finding’s severity and exploitability remain unverified.
Primary source: Anthropic · via ThorstenMeyerAI.com