🔍 Read the full analysis: How A Claude Extension Supply Chain Attack Reached Thousands Of Devices on ThorstenMeyerAI.com

Get the latest gadgets delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
TL;DR
A WIRED headline reports that a supply chain attack placed malicious Anthropic Claude extensions on thousands of devices. The material available here does not identify the extensions, verify the device count, explain what the code did or describe Anthropic’s response.
A WIRED headline, summarized in the original report, says a supply chain attack placed malicious Anthropic Claude extensions on thousands of devices, raising concern about software added to AI tools. The material available here does not include the article’s reporting, so the affected extensions, attack method, confirmed number of devices and any user impact cannot be independently verified.
The headline describes the incident as a supply chain attack, a category of attack that targets a trusted software source or delivery process. It does not say which extensions were involved, where they were distributed, who created them or how malicious code reached users. No specific Claude platform, extension marketplace or product version is identified.
“Thousands of devices” is the scale stated in the headline, but no exact count, measurement period or counting method is provided. The available material does not clarify whether that figure refers to devices where an extension was installed, devices exposed to it, or devices with evidence of malicious activity. Those measures describe different levels of exposure and should not be treated as equivalent.
There is also no information here about the extensions’ behavior, their permissions, or whether they accessed prompts, credentials or files. The material does not say when the issue was discovered, whether the extensions were removed or disabled, or whether Anthropic issued guidance. Those gaps prevent a firm assessment of confirmed harm and what affected users should do.
Risks in Trusted AI Extensions
Extensions can add capabilities to an AI tool, but they also introduce software outside the core product. If malicious code enters a trusted publishing or distribution route, an extension may appear legitimate to users even when it is unsafe. That possibility makes the reported incident relevant to people who install third-party software alongside AI services.
The potential consequences depend on what an extension could access and what it did. The supplied information does not establish whether data was collected, credentials were exposed or devices were otherwise affected. The headline signals a security concern; it does not establish the extent of user impact. Until the affected software and its behavior are documented, readers should distinguish reported exposure from confirmed compromise.
The incident also puts attention on how extension publishers and platforms review, distribute and respond to unsafe software. A clear account of the delivery route and any remediation would help users understand whether the issue was limited to particular extensions or could affect a wider set of integrations. Those details are not present in the material available here.
Products Worth Considering

Bose QuietComfort Wireless Bluetooth Headphones with Active Noise Cancellation, Mic, USB‑C Charging, Deep Bass, 24‑Hour Battery – White Smok
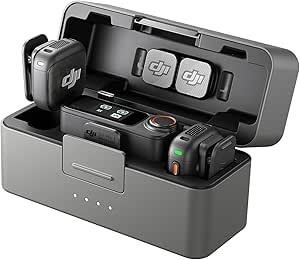
DJI Mic 3 Wireless Microphone System (2 Transmitters, 1 Receiver, Charging Case)

Logitech MX Keys S Wireless Keyboard, Graphite
As an affiliate, we earn on qualifying purchases.
How Extension Supply Chains Can Fail
A supply chain attack targets a trusted part of the process that delivers software, rather than relying only on someone to download a program that is obviously suspicious. In an extension incident, possible routes could include a compromised publisher account, development process or distribution channel. These are general examples, not confirmed explanations for the Claude incident reported in the headline.
The supplied material identifies Claude extensions as the target but names no marketplace, publisher or affected product version. It also provides no incident timeline or prior notice from Anthropic. As a result, the available account supports only a narrow statement: WIRED’s headline reports malicious extensions on thousands of devices, while the mechanics and scale remain unverified here.
““A supply chain attack” put malicious Claude extensions on “thousands of devices.””
— WIRED headline, as relayed in the supplied material
The Count and Impact Remain Unclear
The supplied material does not identify the affected extensions, when they were available, how they reached users or what their code did. It gives no evidence about data access, confirmed victims, the attacker’s identity or Anthropic’s response. The phrase “thousands” has no stated basis, time window or counting method, so it cannot be independently checked from the information provided.
It is also unclear whether the reported figure counts installations, devices that could have been exposed, or devices where investigators observed malicious activity. These are not interchangeable measures. Without that distinction, readers cannot tell whether the report describes a broad potential exposure or a smaller number of confirmed compromises.
No user instructions are included, and the material does not establish whether an affected extension remains available. It is not possible from these details to say whether users need to remove software, change credentials or take another specific action. Any such guidance should come from verified reporting or an official notice that identifies the affected extensions and explains the evidence.
Details Needed for User Guidance
A fuller account from WIRED or an official statement from Anthropic would need to name the affected extensions and explain whether they were removed, disabled or otherwise contained. It should also clarify how the attack reached users and what evidence supports the reported device estimate. Those facts would help distinguish exposure from confirmed malicious activity.
Users need clear, verified advice on checking whether they installed an affected extension and what steps to take if they did. The available material contains no such guidance, so it cannot establish a recommended response. Further reporting should also address whether investigators found data theft or other concrete effects, and whether the incident was limited to particular publishers or distribution routes.
Key Questions
What happened to Claude extensions?
A WIRED headline reports that a supply chain attack put malicious Anthropic Claude extensions on thousands of devices. The supplied material does not describe the extensions or explain how the attack worked.
How many devices were affected?
The headline says “thousands”, but provides no exact count, time period or counting method in the material available here. The figure cannot be independently verified from these details.
What did the malicious extensions do?
The supplied information does not say what the extensions did, what permissions they had or whether they accessed prompts, credentials, files or other user data.
Has Anthropic issued instructions for users?
No Anthropic response or user guidance is included in the supplied material. It also does not identify extensions users could check or confirm whether any were removed.
Does the report confirm that users’ data was stolen?
No. The available material does not establish whether the extensions accessed or took user data, or whether devices suffered other confirmed harm.
Source: ThorstenMeyerAI.com