📊 Full opportunity report: Cybersecurity operations signal monitor: A backdoor in a LinkedIn job offer on IdeaNavigator AI — validation score, market gap, and execution plan.
Play games included with Prime
Start a Prime free trial and play with Amazon Luna on your devices.
Start playingAs an affiliate, we earn on qualifying purchases.
TL;DR
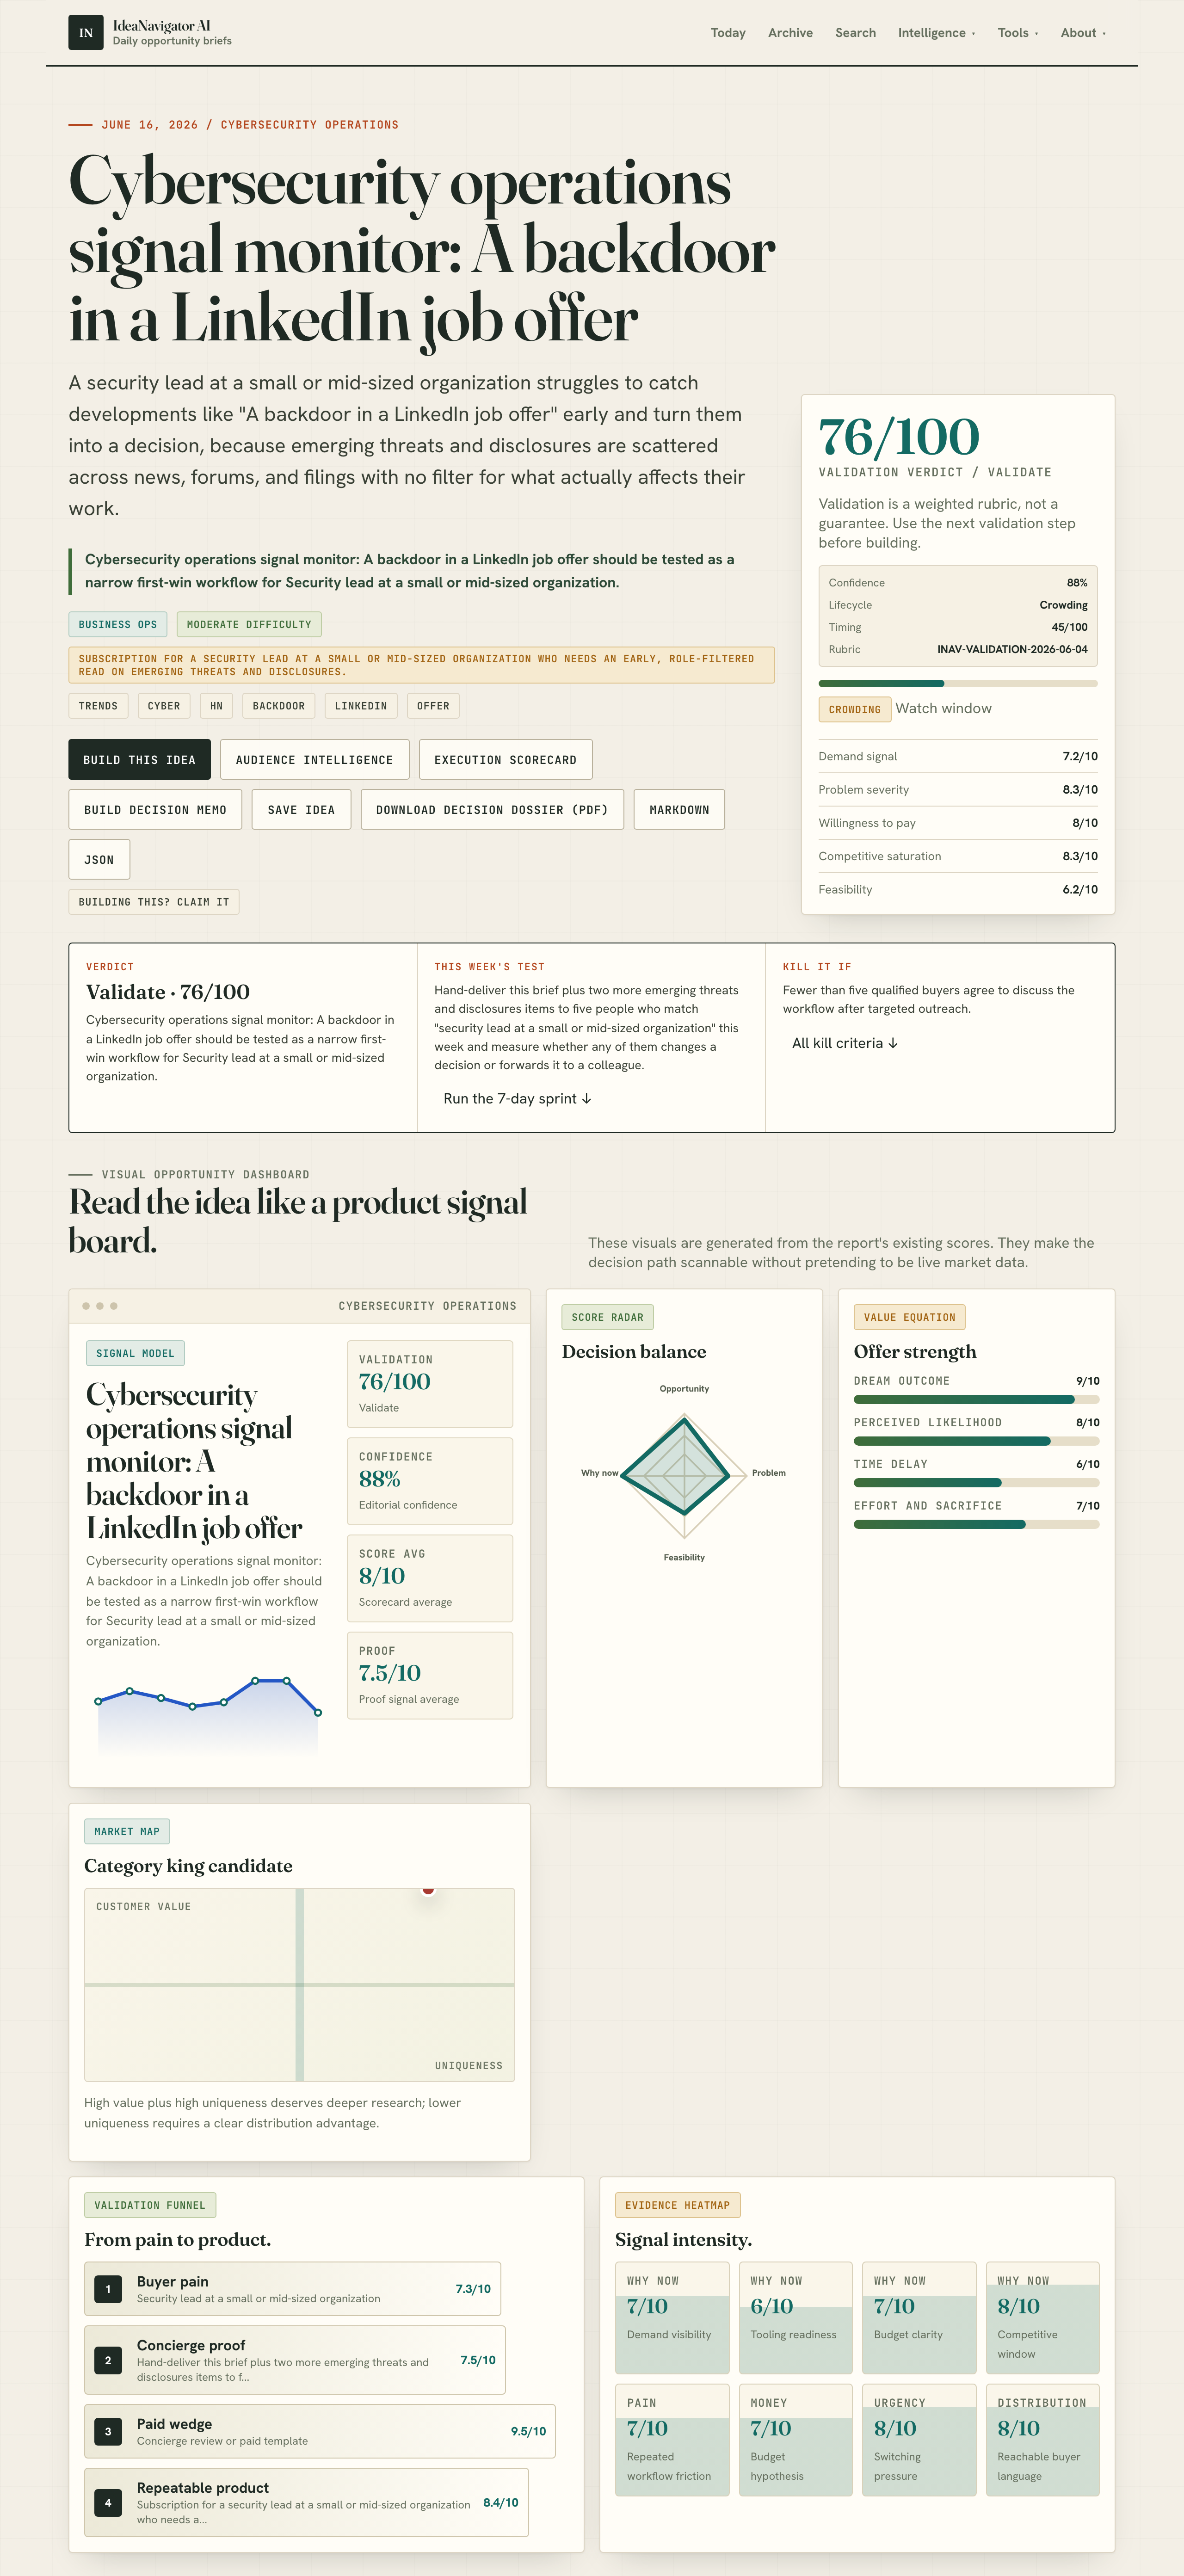
Security researchers detected a backdoor embedded in a LinkedIn job offer, highlighting emerging cyber threats. The development is confirmed and under investigation, with implications for small and mid-sized organizations.
Cybersecurity operations have confirmed the detection of a backdoor embedded in a LinkedIn job offer, raising concerns about targeted cyber threats exploiting social engineering. The finding was announced by cybersecurity analysts and is under active investigation, emphasizing the need for vigilance among organizations.
Recent cybersecurity monitoring has revealed a malicious backdoor hidden within a LinkedIn job posting. The backdoor was identified through automated threat detection tools that scan social media and professional networking sites for emerging threats. Experts confirm that the backdoor could allow unauthorized access to targeted systems if exploited.
While the exact technical details of the backdoor are still being analyzed, initial reports suggest it was embedded using malicious scripts or URL redirection techniques designed to deceive potential victims. The post appeared legitimate but contained embedded code that could compromise security if clicked or interacted with.
Cybersecurity teams are currently working to determine the scope of the threat, whether any organizations have been targeted, and how widespread the malicious campaign might be. No organizations have officially reported breaches linked to this specific incident yet, but the alert underscores the evolving tactics used by threat actors to exploit social engineering channels.
Implications for Organizational Security and Threat Detection
This discovery highlights the increasing sophistication of cyber threat actors who leverage social engineering and social media platforms to infiltrate organizations. The presence of a backdoor in a widely used professional networking site like LinkedIn underscores the importance for security teams to monitor social media for emerging threats actively.
For small and mid-sized organizations, which often lack extensive cybersecurity resources, such threats pose a significant risk. Early detection and rapid response can prevent breaches, data theft, or system compromise. The incident also emphasizes the need for awareness training around social engineering and suspicious online activity.
cybersecurity threat detection tools
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Over the past year, cybersecurity analysts have observed a rise in malicious campaigns exploiting social media platforms, including LinkedIn, Twitter, and Facebook. Threat actors embed malicious links or scripts within seemingly legitimate posts, job offers, or messages to lure targets into clicking malicious content.
This specific incident follows a pattern of targeted attacks aimed at organizations with valuable data or access. Attackers often use social engineering to bypass traditional security measures, making social media a critical vector for threat delivery. The detection of this backdoor is part of a broader trend of increasing threat sophistication and targeted campaigns.
“The backdoor embedded in this LinkedIn post demonstrates how social engineering is evolving to bypass conventional defenses. Organizations must enhance their monitoring of social media threats.”
— an anonymous cybersecurity researcher
social engineering awareness training
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Details of Targeted Organizations and Scope of the Threat
It is not yet clear how many organizations have been targeted or if any breaches have occurred as a result of this backdoor. The full technical details of the backdoor’s design and deployment are still under analysis, and authorities have not released information on whether the threat is ongoing or contained.
network security monitoring software
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Ongoing Investigation and Recommended Security Measures
Cybersecurity teams are actively analyzing the malicious code and monitoring for additional instances. Organizations are advised to scrutinize social media postings related to job offers and implement enhanced threat detection measures, including social media monitoring tools and employee awareness training. Further updates are expected as investigations progress and more details become available.
As an affiliate, we earn on qualifying purchases.
Key Questions
What exactly is a backdoor in a cybersecurity context?
A backdoor is a hidden method of bypassing normal authentication or security controls, allowing unauthorized access to a system or network.
Organizations should monitor social media channels for suspicious activity, train employees on social engineering risks, and implement security tools that flag malicious links or scripts.
Has any organization been compromised by this backdoor?
There are no confirmed reports of organizations being compromised yet; investigations are ongoing to determine the scope of the threat.
What should employees do if they encounter suspicious job offers on LinkedIn?
Employees should verify the authenticity of job postings through official channels, avoid clicking on suspicious links, and report potential threats to their security team.
Will there be more updates about this threat?
Yes, cybersecurity teams are actively investigating, and further details are expected to be released as the situation develops.
Source: IdeaNavigator AI
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.